On this page
- 01Key takeaways
- 02Why must the decision stay with you?
- 03What should happen in the first 72 hours?
- 04What should your processor contract require?
- 05When does a breach not need reporting?
- 06What does this look like in practice?
- 07Breach decision checklist
- 08Next step
- 09Sources and further reading
- 10Frequently asked questions
Key takeaways
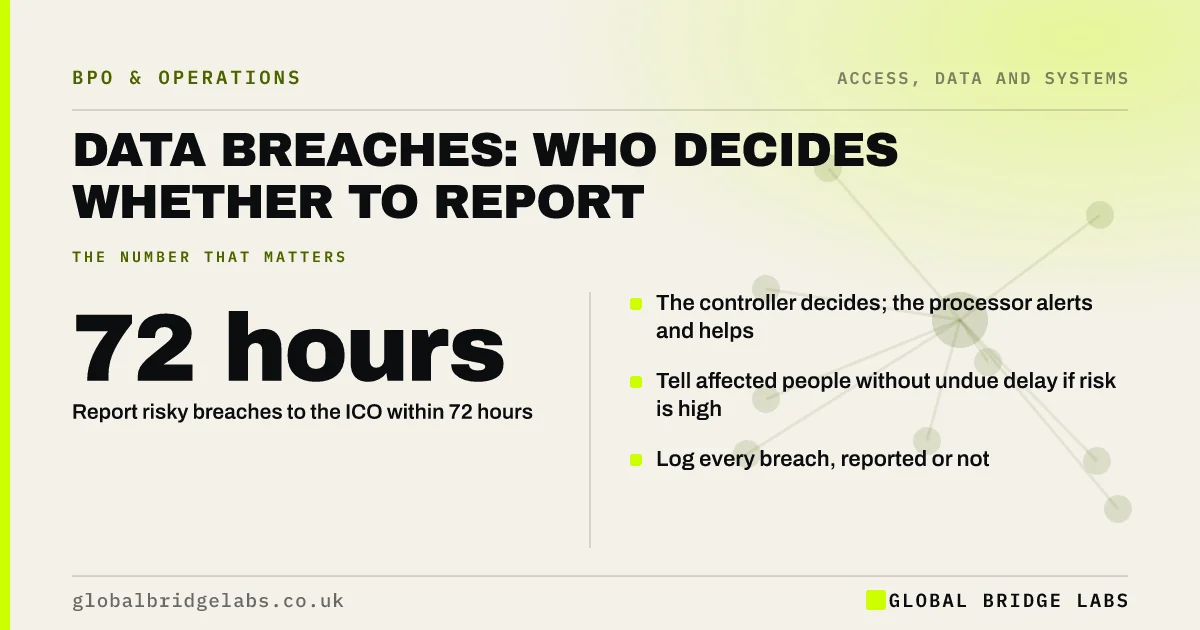
Who decides to report a data breach? The data controller, which is your business, not your provider. Where a breach is likely to risk people's rights and freedoms, you must report it to the ICO within 72 hours of becoming aware, and tell affected people if the risk is high. Your processor must tell you without undue delay.
- The controller decides; the processor alerts and helps.
- Report risky breaches to the ICO within 72 hours.
- Tell affected people without undue delay if risk is high.
- Log every breach, reported or not.
Want a one-page breach decision plan? Message us on WhatsApp.
Chat on WhatsApp →Why must the decision stay with you?
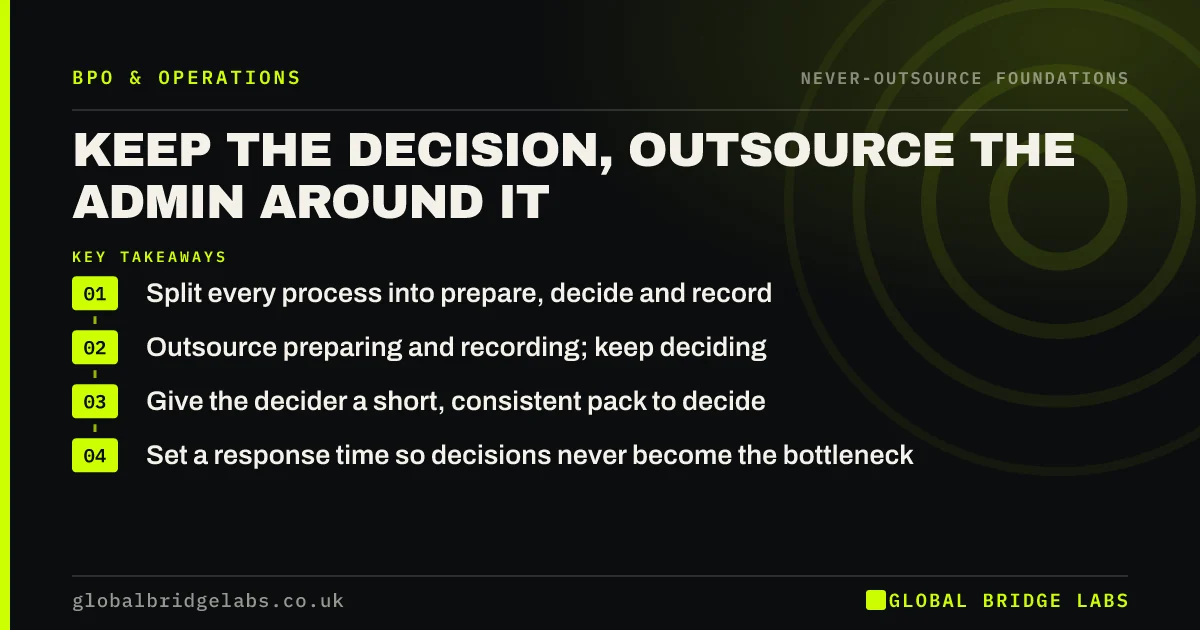
Because the duty to report sits with the controller, and the decision weighs legal risk, customer trust and what to say publicly. A provider may understate a breach it caused, or overreact. A named person in your business, with advice, should judge the risk and decide.
What should happen in the first 72 hours?
The clock starts when you become aware, which can include when your processor tells you.
- Contain the breach and secure systems.
- Establish what data, how many people and what risk.
- Decide whether to report to the ICO.
- Decide whether to tell affected individuals.
- Record the facts, decision and reasons.
What should your processor contract require?
Notification to you without undue delay, with the details you need to assess risk, plus help with containment, investigation and any notifications. Agree a target, such as within 24 hours of the provider becoming aware, so your 72 hours are not used up waiting.
When does a breach not need reporting?
When it is unlikely to result in a risk to individuals, for example a misdirected email containing no sensitive data that is promptly deleted. You must still log it and record why you decided not to report. The ICO's self-assessment tool helps with the judgement.
What does this look like in practice?
A pattern we see: a provider mentions a 'minor incident' in a monthly report, weeks after it happened. Contracts with a 24-hour notification rule and a named internal decision-maker keep reporting within the legal window.
Breach decision checklist
- Name a breach decision-maker and deputy.
- Require providers to notify within 24 hours.
- Use the ICO self-assessment to judge risk.
- Report within 72 hours where required.
- Log every breach and decision.
Next step
Check your main provider contracts for a breach notification time. If none is stated, agree one this month.
Message us on WhatsApp, or book a 30-minute consultation.
Chat on WhatsApp →Sources and further reading
- Report a breach · Information Commissioner's Office
- Contracts and liabilities between controllers and processors · Information Commissioner's Office
Frequently asked questions
Who is responsible for reporting a data breach to the ICO?
The data controller. If your provider is a processor, it must tell you without undue delay, but your business decides whether the breach must be reported to the ICO and to affected individuals, and makes the report.
How long do you have to report a data breach?
Where a breach is likely to result in a risk to people's rights and freedoms, report it to the ICO within 72 hours of becoming aware of it. If you do not have all the details, report what you know and provide more later.
Do all data breaches have to be reported?
No. Only breaches likely to result in a risk to individuals must be reported to the ICO, and individuals must be told where the risk is high. Every breach should still be recorded internally with the reasons for your decision.
Written by
Global Bridge Labs (GBL) is a UK–Sri Lanka partner for social media, websites and BPO. Everything here comes from client delivery, not theory.